
A researcher from Upguard found a leaky AWS bucket, which was exposing the sensitive data of Godaddy’s customers available publicly over the internet. The leaky or unsecured AWS bucket contains configuration information such as hostname, operating system, workload, AWS region, memory and CPU specs, and much more.
A security firm, Upguard found the publically readable Amazon S3 bucket contains several spreadsheet files that contain data about Data Legend, GDDY Machine Raw Data, Summary, Compute, Storage, Instance Mapping, Spot and Price List.
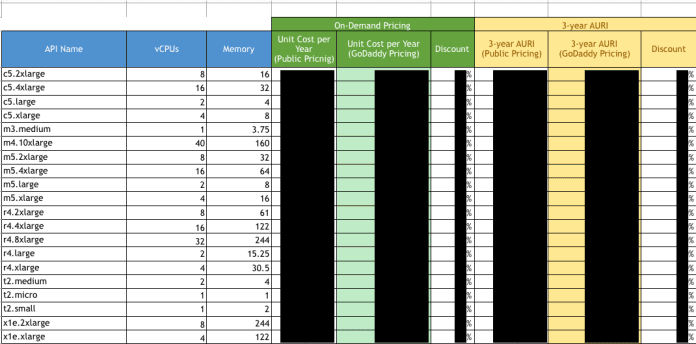
Upguard noted that the leaked data doesn’t expose any sensitive information that stored in the servers, but this configuration leaks could be used by the cybercriminals to perform various types of attacks. It can also give a much information to attackers to launch a high profile attack.
Godaddy is the world’s leading domain registrar with over 18 million customers with over 76M domain names. Upguard found this unsecured amazon S3 bucket on June 19th and they reported this issue to Godaddy on June26th.
Amazon’s S3 storage buckets are private by default, only the permitted
users can access the bucket, but due to misconfiguration’s the data are
exposed to public access.
This was not the first time that
UpGarud found unsecured AWS S3 buckets. Earlier also they have found
many buckets of different high profiled organization which are exposing
sensitive information. Lastly, Upguard reported another leaky bucket of size 157GB, that was exposing sensitive data from top manufacturer including Ford, Toyota, GM, Tesla.
Community Discussion
Join the conversation. Ask questions, share solutions, and help others.
Be the first to start the discussion!