
Organisations running Citrix NetScaler appliances began taking them offline on Saturday after security teams relayed a warning about two unpublished remote code execution flaws, a warning neither Citrix nor the Dutch National Cyber Security Centre has published.
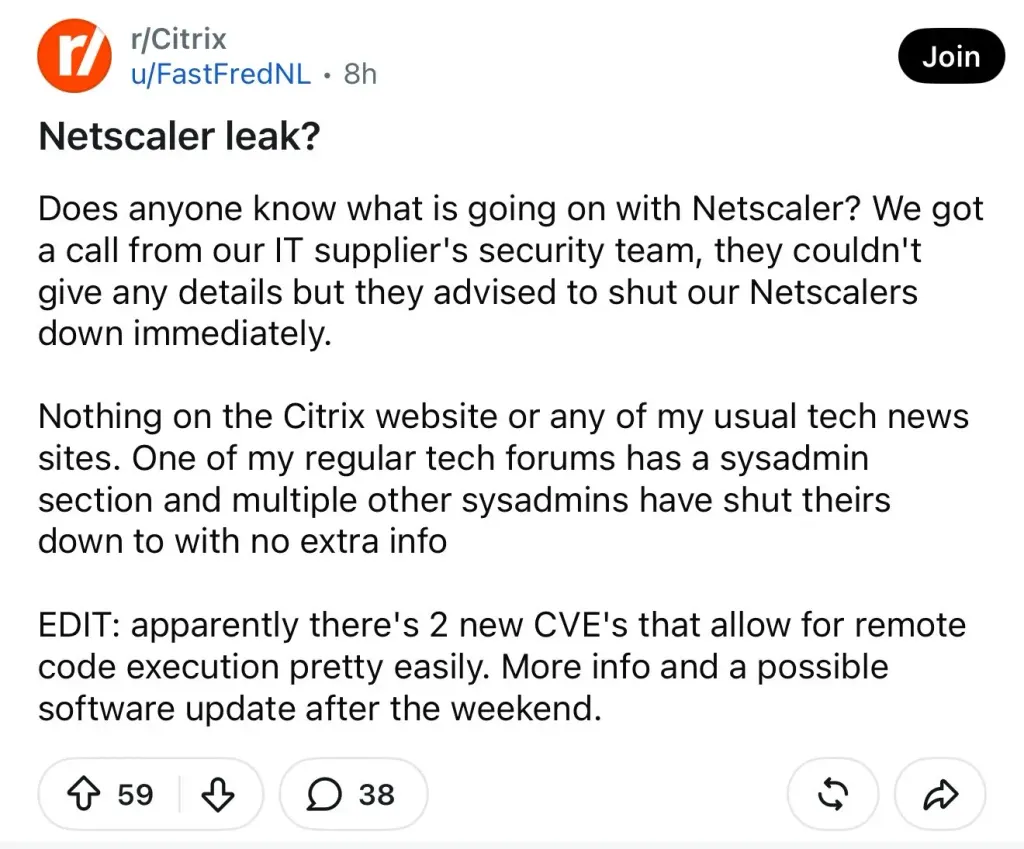
The reports surfaced in a Reddit thread on r/Citrix titled “Netscaler leak?”, which had 75+ upvotes and more than 50+ comments by Saturday evening. The thread’s author, a user named FastFredNL, said their IT supplier’s security team called and advised an immediate shutdown but gave no details.
FastFredNL said the supplier normally advises customers to update quickly or change a setting as a temporary mitigation. This time the supplier said, “this is a big one and there’s no fix yet, shut it down.”
According to FastFredNL, the two flaws allow remote code execution with little effort and have not yet been assigned CVE IDs or severity scores. More information and possibly a software update are expected after the weekend, the user added.
Who is telling admins to shut NetScaler down?
FastFredNL said the supplier gets its information directly from NCSC-NL. The user’s understanding is that the agency reported the flaws to Citrix and then advised organisations to power down rather than wait for a fix. Cyber Kendra has not confirmed that account.
Another administrator in the thread said their organisation shut its NetScalers down based on an NCSC notification. The notice arrived through the organisation’s CERT team rather than the NCSC website, and management made the decision. A third said their appliances were offline while they waited for word from their CSIRT, the NCSC or Citrix.
Other administrators received nothing. One found no notice on the NCSC site and no email from the agency, and said an earlier comment mentioning the notice had been deleted without explanation. Another said their Citrix technical account manager had heard nothing.
FastFredNL rejected suggestions that the warning concerns CVE-2026-19490, a critical authentication bypass that Citrix patched on August 19 and that has been exploited since September 3. If it did, the user said, the supplier would have named it.
Has Citrix or the NCSC confirmed new NetScaler flaws?
Not as of publication. The most recent NetScaler bulletin Cyber Kendra found is CTX696939, which covers CVE-2026-19489 and CVE-2026-19490. NCSC-NL’s newest public advisory, NCSC-2026-0318, covers the same two flaws, and the agency raised its rating to high.
With no advisory published, it is unknown which NetScaler configurations or builds are affected, or whether appliances on the latest fixed builds, 14.1-73.32 and 13.1-63.21, are exposed.
The NetScaler reports came the same weekend that Kiteworks asked customers to shut down its file-sharing servers over a possible imminent attack. Kiteworks’ CISO cited intelligence from law enforcement, while the company’s press release refers to federal intelligence authorities and a nine-hour window. Several Reddit users asked whether the two warnings are connected. Nothing published so far links them.
The Dutch agency has advised a Citrix shutdown before. In January 2020, NCSC-NL told organisations to consider switching off Citrix ADC and Gateway during attacks on CVE-2019-19781, after concluding that Citrix’s interim mitigations did not work reliably. Two government ministers approved that advice, which, unlike the current warning, was issued publicly.
In July 2025, NCSC-NL sent confidential alerts to organisations it believed had been hit through CVE-2025-6543, weeks before confirming that the flaw had been exploited as a zero-day against critical Dutch organisations. More recently, Citrix first described CVE-2026-8452 as a denial-of-service bug, until watchTowr showed that it allows root-level code execution.
What should NetScaler admins do before Monday?
Users in the thread suggested stopgaps for teams that cannot go offline: blocking internet access and allowing only a temporary list of employee addresses, or disabling DTLS and watching the crash dumps folder.
Note: None of this guidance comes from Citrix, and its effect on the unpublished flaws is unknown. Restricting inbound access to trusted IP ranges matches the interim advice Mandiant gave during earlier NetScaler attacks.
Shutting an appliance down does not remove an attacker who is already inside it. In 2025, NCSC-NL warned that intruders could keep access after patches were applied, and it published compromise-check scripts for NetScaler images and core dumps.


Community Discussion
Join the conversation. Ask questions, share solutions, and help others.
Be the first to start the discussion!