
Managed detection and response has been a crowded category for years, and most of the buyer guides written about it are difficult to tell apart. They list the same providers, repeat the same capability claims, and stop short of the questions that actually determine whether a contract works.
The five providers below are among those most often shortlisted in enterprise evaluations. The profiles draw on published positioning and documented customer feedback rather than proprietary testing, and each one is examined against the operational questions that surface at renewal rather than during the sales cycle: what gets a full investigation, what happens to detections your own team wrote, what the artifact looks like when an alert comes back to you, and who is permitted to act at three in the morning.
The comparison rates each provider on a single axis that rarely appears on a pricing page. What actually happens to an alert after it fires?
How to Read an MDR Offering
Most of the variation between providers shows up at the alert level rather than the marketing level. A few dimensions do most of the work separating one offering from another, and most are difficult to see until you are already under contract.
What counts as investigated. Every provider will tell you they investigate alerts. The operational question is what that word covers. For some, investigation means running an alert through a tuned filtering pipeline, adding threat intelligence enrichment, and routing the result to auto-close or customer escalation.
For others, it means an analyst pulls query results, cross-references endpoint telemetry, walks the authentication chain, and writes a conclusion with evidence attached. The gap between those definitions is enormous, and it is rarely made explicit.
The middle of the severity distribution. Critical alerts get hands-on treatment from almost every provider that stays in business. Informational alerts get bulk-closed by almost every provider that stays in business. The interesting question is what happens to medium-priority alerts, which make up the bulk of volume and occasionally hide the early indicators of a real intrusion. This is where providers diverge most.
Custom detection treatment. If your team writes its own rules, correlation logic, or behavioural detections, how does the provider handle the alerts those rules generate? Some investigate them with the same process as vendor-supplied detections. Many treat them as out of scope and forward them back. This gap widens as a detection program matures and custom content grows as a share of total volume.
The artifact you get back. When an alert returns to your team, what does it look like? A severity label and a link to the raw event, a short summary, or a documented investigation showing what was queried, what came back, and how the reasoning moved from evidence to conclusion? The answer determines how much re-investigation your team performs after each escalation, which is a real and recurring cost.
Who can take action and when. Containment authority varies widely. Some providers isolate hosts and revoke sessions unilaterally on confirmed threats. Others require explicit approval for every step. The difference matters most during an active intrusion at an inconvenient hour, which is also when it is least likely to have been tested during evaluation.
Several of these dimensions have no clean vendor-level answer, because they are properties of the shared-analyst delivery model itself. One team serving many customer environments bounds investigation depth, contextual knowledge, and custom content handling in ways that switching providers within the category does not fix. The better providers operate efficiently within those constraints. None of them removes them.
ESET
ESET approaches managed detection from an unusual position among providers in this comparison, in that it builds the detection technology underneath the service rather than assembling third-party tools. ESET Inspect, the vendor’s XDR layer, feeds a 24/7 analyst team, and the company has contributed to the MITRE ATT&CK knowledge base for years rather than only mapping detections against it.
Two things distinguish the offering at the operational level. The first is specificity where competitors stay general. ESET publishes a six-minute mean time to respond, measured from initial detection to first action taken, rather than resting on a 24/7 availability claim. That figure is checkable against the contract in a way that a general commitment is not.
The second is the entry threshold. The service starts at 25 devices with no commitment, which is considerably lower than most managed SOC offerings require, and puts it within reach of organisations that would otherwise be quoted out of the category entirely. Two tiers are available: core MDR and MDR Ultimate, which adds retrospective threat hunting, digital forensic incident response, and a dedicated incident response lead.
The constraints are worth naming. Pricing is available on request rather than published, so the comparison against providers with transparent tiers requires a conversation before it can be made. The service is also strongest where the endpoint layer is already ESET, which is the same coupling that applies to most vendor-originated MDR offerings and is a genuine consideration in a mixed estate.
On the custom detection question, as with most providers in this category, the treatment of rules your own team authored is worth establishing explicitly during a proof of concept rather than assuming parity with vendor-supplied content.
ESET fits organisations that need coverage now rather than after a lengthy SOC build, that value a published response figure over a general commitment, and whose scale sits below the threshold most managed SOC providers will quote for.
Arctic Wolf
Arctic Wolf runs one of the largest MDR operations in North America on a concierge delivery model. Each customer is assigned a named Concierge Security Team that owns monitoring, investigation, escalation and periodic strategic reviews through the same people.
The concierge relationship is both the value proposition and the structural constraint. A named team that stays with an account builds real institutional knowledge, including which service accounts behave unusually by design and which alerts the customer has explicitly deprioritised. That knowledge lives inside the provider rather than the customer, so if the relationship ends, the context resets to zero and the next provider starts cold.
At the alert level, two patterns are worth testing during evaluation. Direct analyst access to raw data for independent verification tends to be limited, so validating an escalation by running the same queries is not always frictionless. And detections authored by the customer frequently route differently from detections originating in the provider’s own content library.
Arctic Wolf is strongest in mid-market environments where trading operational control for turnkey coverage makes sense, and where a dedicated named team fills a gap that internal staff cannot cover.
eSentire

eSentire’s Atlas platform anchors a service built around fast containment. The positioning is response-forward, meaning the provider takes action on confirmed threats rather than returning a recommendation for the customer to execute.
Response authority is the clearest differentiator here. For customers who sign the containment authorisation, the provider isolates hosts, revokes sessions and terminates tokens without waiting for approval on each action. That changes the economics of an alert arriving outside business hours in a meaningful way. The in-house threat research function also produces original intelligence that feeds back into what gets alerted on.
The caveats are tier-specific. Investigation depth, custom detection coverage and response authority all vary by package, and the published tier matrix does not always make the investigation-level implications obvious. A customer on a lower tier receives a substantively different service from one on the highest.
eSentire fits teams that have made a deliberate decision to delegate response authority to the provider, particularly where containment speed is tied to a regulatory obligation.
ReliaQuest
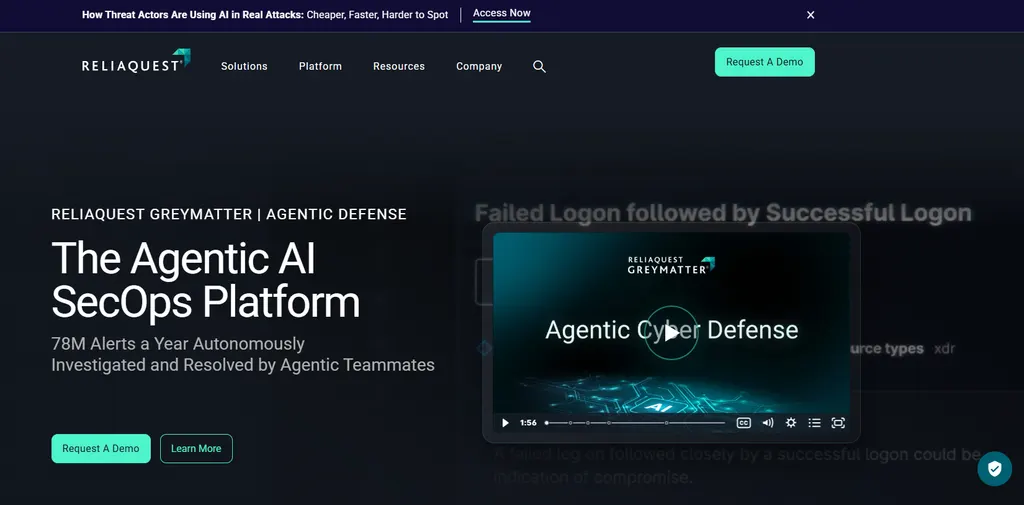
ReliaQuest’s GreyMatter platform sits above a customer’s existing tool stack as an operations layer, connecting to SIEM, EDR, cloud and identity sources rather than replacing them. Recent iterations lean heavily on agentic automation for work traditionally assigned to entry and mid-tier analysts.
The relevant question is what that automation does at the alert level. For straightforward cases, including commodity phishing and benign impossible travel, the automation handles investigation and closure without human involvement. More ambiguous cases route between the agents and the human analyst pool behind the platform. Escalations arrive with investigation notes and recommended actions rather than raw alerts, which removes some re-investigation work.
Two things to weigh. The platform’s ambition extends well beyond investigation and response, covering attack surface management, digital risk protection and threat hunting in the same footprint. Paying for that breadth makes sense only if you plan to use meaningful portions of it, and teams shopping specifically for investigation capacity frequently find the contract value disproportionate to that narrower need. Pricing is reported to sit above the mid-market median, which filters the profile toward larger enterprises.
ReliaQuest fits enterprises with genuinely heterogeneous tool environments that want a single operations layer across them, rather than teams looking for a focused MDR replacement.
Expel
Expel built its practice around a transparent delivery model that places customers inside the same investigation workbench its analysts use. Automated enrichment handles early-stage evidence assembly, while analysts make the calls on verdicts and escalations.
The transparency is real and it matters. When an analyst escalates an alert, the customer can open the investigation and see the sequence of queries, pivots and evidence that led to the conclusion. That removes the most common source of friction in these relationships, which is guessing whether an escalation was handled the way your own team would have handled it.
The structural limit is the delivery model. Investigation depth per alert is bounded by analyst capacity, which is bounded by headcount and queue volume across the full customer base. Alerts requiring deep environmental context, a correlation that depends on understanding a nonstandard deployment pipeline for instance, can still route back with partial investigation and a request for more context.
Expel works well for teams that want to watch their provider work, and occasionally disagree with a verdict in the same platform where it was rendered.
Questions Worth Asking at Renewal
The questions that separate providers are not the ones asked during the sales cycle. They are the ones that can only be answered from a year of operational data. Five are worth putting in writing before the next term begins.
Ask what share of alerts received a full documented investigation in the previous year, as distinct from filtering, enrichment and escalation. Most buyers sign with an implicit assumption about this number and never measure it.
Ask how your custom detections fared. If the provider investigated fewer than half of them, that gap has been present throughout and will persist through the next term unless something structurally changes.
Ask about escalation-to-incident latency for the genuine incidents that landed during the year. That is the response time that matters, and it tends to look different from the average time-to-triage reported in marketing materials.
Ask how many different analysts have worked your account in the past twelve months, and what turnover looks like. Context loss at handoff is a consistent source of friction and a leading indicator of escalation quality declining.
Ask what you own at contract end: detection content, investigation history, tuning work. This matters considerably more than most buyers realise until they are trying to migrate, and it belongs in the same category as any other third-party risk assessment, where the supervisory expectation is increasingly that outsourcing a function does not outsource responsibility for it. That is one reason some organisations bring in a virtual CISO to keep oversight of external security providers.
MDR in 2026: A Real Category with Real Limits
MDR exists because round-the-clock SOC staffing is operationally and economically out of reach for most organisations. Outsourcing investigation capacity to a provider running a shared analyst pool is a legitimate answer to that constraint, and across a broad section of the market, it remains the right one. The category is not in decline. It is maturing.
What has changed is that the structural ceilings of the model are now more visible. Detection programmes have matured, custom content has grown as a share of alert volume, and the distance between an alert having been investigated and it having been investigated the way your own team would have is no longer theoretical.
For most buyers, the practical response is not to abandon the category but to evaluate it more precisely. Establish what a provider means by investigation before signing, test the treatment of your own detections during a proof of concept rather than after, and write the renewal questions into the contract now, while you still have leverage.
The providers that answer those questions directly have told you something useful. So have the ones that deflect.


Community Discussion
Join the conversation. Ask questions, share solutions, and help others.
Be the first to start the discussion!