
A new study from researchers at the Citizen Lab and Princeton University has exposed a troubling trend in the network security of Android apps, particularly those popular in China.
According to the research paper, the team has analyzed 1,699 top apps from the Google Play Store and 817 from the Xiaomi Mi Store.
It found that 47.6% of Mi Store apps rely on insecure proprietary network encryption, compared to just 3.51% of Google Play Store apps. This widespread use of flawed custom protocols, instead of standard Transport Layer Security (TLS), leaves sensitive user data vulnerable to interception.
The team developed WireWatch, an automated tool that scrapes app stores, interacts with app interfaces, captures network traffic, and clusters it to identify non-standard encryption.
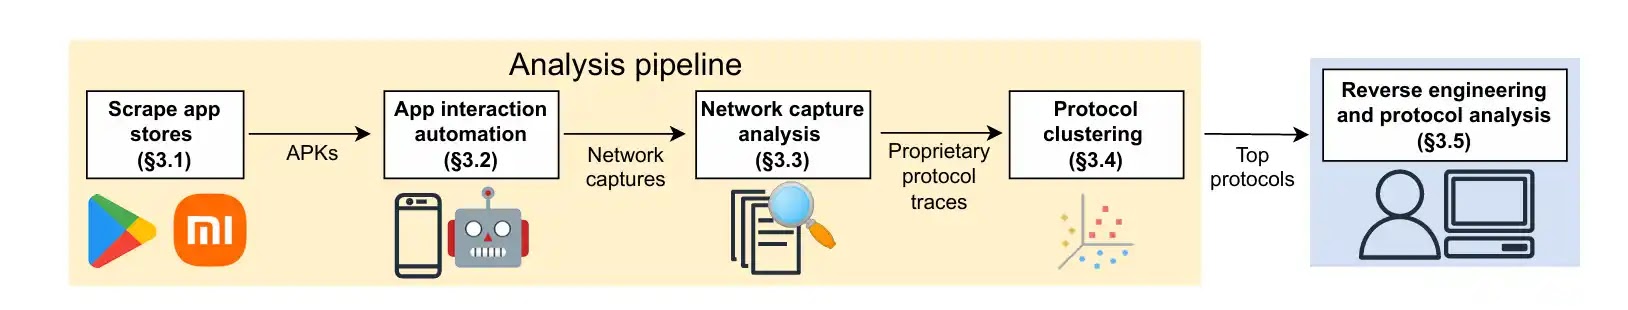 |
| Outline of WireWatch design |
Their analysis showed that apps from the Mi Store, often developed for the Chinese market, frequently employ proprietary schemes that are poorly designed.
“Ultimately, WireWatch reveals that a large portion of massively popular applications are using insecure proprietary network protocols to encrypt sensitive user data,” the researchers note.
These apps, with a cumulative 130 billion downloads, include household names supported by SDKs from companies like Alibaba and Tencent.
Specific vulnerabilities were stark. Eight of the nine most common protocol families—such as Alibaba mPaaS and Tencent DNSPod—sent decryptable requests due to static keys or flawed encryption methods like AES-CBC without proper padding.
For instance, Alibaba’s mPaaS SDK, used by apps like UC Browser, encrypts browsing data with a static key stored in an image file, easily extractable by attackers.
This exposes user information like browsing history and device metadata to network eavesdroppers or man-in-the-middle attacks. Additionally, 49.1% of Mi Store apps fail to validate TLS certificates, amplifying the risk.
The implications are significant, especially given the scale—apps with over a billion downloads are disproportionately affected.
The researchers disclosed these issues to vendors, with some, like iQIYI and Tencent, already deploying fixes. One researcher noted, “The continued usage of poorly designed custom cryptography is still a systemic issue across the most popular mobile apps in the world.”
Read the full study here (PDF).

Community Discussion
Join the conversation. Ask questions, share solutions, and help others.
Be the first to start the discussion!