
[Updated: March 30, 2026 — Score revised from 9.8 to 7.0. Original story below.]
On Sunday, Telegram’s official account dismissed a newly disclosed zero-click vulnerability as fabricated, directly challenging researchers at Trend Micro’s Zero Day Initiative (ZDI) who had just filed a near-maximum severity bug report against the platform.
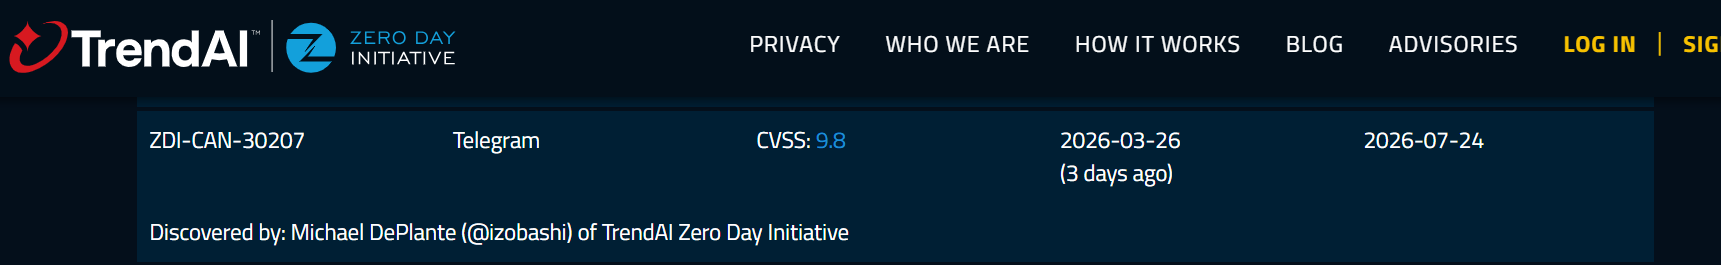
The vulnerability, tracked as ZDI-CAN-30207, was discovered by researcher Michael DePlante (@izobashi) of Trend Micro’s Zero Day Initiative and carries a CVSS v3 score of 9.8 out of 10 — essentially the ceiling of critical. It was reported to Telegram on March 26, 2026.
Researchers describe an attack vector rooted in animated stickers: specially crafted media files that, once delivered, automatically trigger the execution of malicious code. No confirmation, no tap, no scroll.
The system processes the files to generate previews, and that preview-generation stage is precisely where the attack fires. A successful exploit could grant an attacker total control — stealing data, modifying files, and crashing services — affecting both Telegram for Android and Linux.
On March 30, Trend Micro’s Zero Day Initiative quietly downgraded the severity score of ZDI-CAN-30207 from 9.8 to 7.0, citing server-side mitigations that Telegram described during the disclosure process. ZDI posted on X:
“We have adjusted the scoring on the advisory to reflect server-side mitigations that the vendor described during the disclosure process.”
But the researcher who found the flaw, Michael DePlante (@izobashi), made one thing crystal clear: the vulnerability is not gone. In a follow-up post on X today, DePlante wrote:
“To be clear, the vuln does exist in the client-side code. During the disclosure process, Telegram described that all stickers are validated server-side; therefore, exploitability is significantly narrower than my initial scoring reflected.“
Italy’s national CSIRT (Computer Security Incident Response Team) took the report seriously enough to issue a formal alert (AL01/260328/CSIRT-ITA), warning that standard “disable auto-download” settings offer no protection, since sticker parsing happens at the system level during preview generation. They recommended that users without an urgent need for the app consider temporarily uninstalling it and switching to Telegram Web via a modern browser as a sandboxed alternative.
Today, Telegram wrote on X:
“This flaw does not exist. This researcher falsely claims that a corrupted Telegram sticker could be used as an attack vector — which completely disregards that all stickers uploaded to Telegram are validated by its servers before they can be played by Telegram apps.“
Telegram has until July 24, 2026, to patch the issue before ZDI’s 120-day responsible disclosure clock runs out and full technical details become public. The company’s denial, however, does not pause that clock — and ZDI has not withdrawn the filing.
The dispute puts users in an uncomfortable middle: ZDI is a well-regarded program with a documented track record, while Telegram’s server-side validation argument is plausible but unverified by independent parties. Experts note that the CVSS vector — network-reachable, low complexity, no privileges required, no user interaction — places this in the most dangerous category if the flaw holds up under scrutiny.
What you should do right now: Keep Telegram updated. In Settings → Privacy and Security → Messages, restrict incoming messages to contacts only or Premium users. (Note: This option is only available to Premium users), which means you are vulnerable (by default/not paying for premium) if the flaw gets confirmed.
If you’re on Android or Linux and can’t verify your app version is patched, consider using Telegram Web in Chrome or Firefox as a precautionary step until this dispute is resolved.
This story will be updated if ZDI or Telegram issues further technical statements.


Community Discussion
Join the conversation. Ask questions, share solutions, and help others.
Be the first to start the discussion!