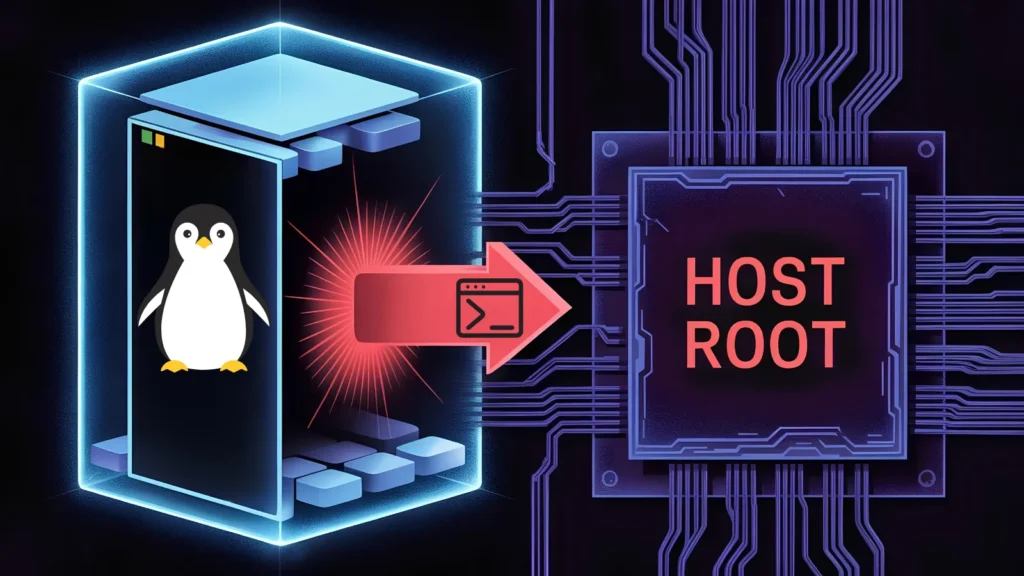
A public exploit for CVE-2026-80521, a use-after-free flaw in the Linux kernel’s AF_UNIX socket code, lets an unprivileged process break out of a Docker or Kubernetes container and take root on the host. Security firm depthfirst released the code on September 22, and Ubuntu still lists its newest release, Ubuntu 26.04 LTS, as vulnerable.
The flaw carries a CVSS v3.1 score of 7.8 (High), and Ubuntu rates it Medium priority. It is a race condition (two kernel operations overlap when they must not) in the garbage collector that cleans up UNIX sockets that pass file descriptors to one another via SCM_RIGHTS messages. No attacks exploiting the flaw have been reported.
How the CVE-2026-80521 Exploit Works
When a process sends file descriptors over a UNIX socket, the kernel publishes the new reference edges to the garbage collector just before it queues the message. If the collector runs inside that gap, it can mark a group of sockets as dead and free part of it, while one socket survives, held alive by the not-yet-queued message. The freed unix_vertex object stays linked in the survivor’s cached scc_entry ring, so the next collection pass walks straight into freed memory.
In its write-up, depthfirst researcher Zhenpeng (Leo) Lin says the company found the bug with dfs-large1, its in-house vulnerability-hunting AI model, and used it to win a Google kernelCTF slot on July 24, 2026. The upstream kernel fix, which unlinks scc_entry before the vertex is freed, credit Kyle Zeng with the report.
AF_UNIX sockets sit underneath systemd, Docker, and local database connections, and the syscalls that reach them are allowed by default Docker and Kubernetes seccomp profiles. That puts the bug within reach of a non-root process in a standard container, and depthfirst says sandboxes such as nsjail, Firejail, and Bubblewrap are exposed as well.
Which Ubuntu Versions Are Vulnerable?
Ubuntu’s CVE-2026-80521 tracker, last updated September 21, marks the main linux package on 26.04 LTS as “vulnerable, work in progress” and on 24.04 LTS as vulnerable, along with the AWS, Azure, and GCP kernels for both releases. The stock 22.04 LTS kernel is not affected, but the 6.8-based HWE and cloud kernels offered for 22.04 are. DepthFirst also published a second container escape exploit targeting CVE-2026-52910 for Ubuntu 24.04.
Until Canonical ships a fixed kernel, administrators running multi-tenant or untrusted containers on these releases have no package updates to apply. depthfirst recommends moving those workloads to microVM runtimes such as Firecracker or Kata Containers, which give each workload its own kernel, so a kernel exploit stays within that instance. When patched kernels are available, hosts need to reboot before the fix takes effect.
A Run of Linux Kernel Container Escapes
CVE-2026-80521 adds to a crowded year for kernel privilege escalation. In July, Nebula Security researcher VEGA disclosed GhostLock (CVE-2026-43499), a 15-year-old rtmutex use-after-free triggered through futex calls that also enables container escapes and earned $92,337 through kernelCTF. In the same month, public exploit code was released for Bad Epoll (CVE-2026-46242), a race condition use-after-free in the epoll subsystem that affects kernels 6.4 and newer.
depthfirst counts 5,976 Linux kernel CVEs published in 2026 through mid-September, with August alone accounting for 1,650.
Community Discussion
Join the conversation. Ask questions, share solutions, and help others.
Be the first to start the discussion!