Uncategorized
nginx2root: NGINX HTTP/2 RCE Flaws (CVE-2026-123007) Patched
CVE-2026-123007 affects every NGINX release since 1.9.5 with HTTP/2 on; fixes are in 1.30.7 and 1.31.9, and Rapid7's exploit is public.


We couldn't find any blog articles matching your search. Try searching for other cybersecurity topics or keywords.
CVE-2026-123007 affects every NGINX release since 1.9.5 with HTTP/2 on; fixes are in 1.30.7 and 1.31.9, and Rapid7's exploit is public.
CVE-2026-123007 affects every NGINX release since 1.9.5 with HTTP/2 on; fixes are in 1.30.7 and 1.31.9, and Rapid7's…
A 65-character Base64 string corrupts the Java heap on AVX-512 servers. Calif got pre-auth RCE in Jira, Jenkins…
Let’s explore why online services still rely on SMS codes, the problems created by using one number for…
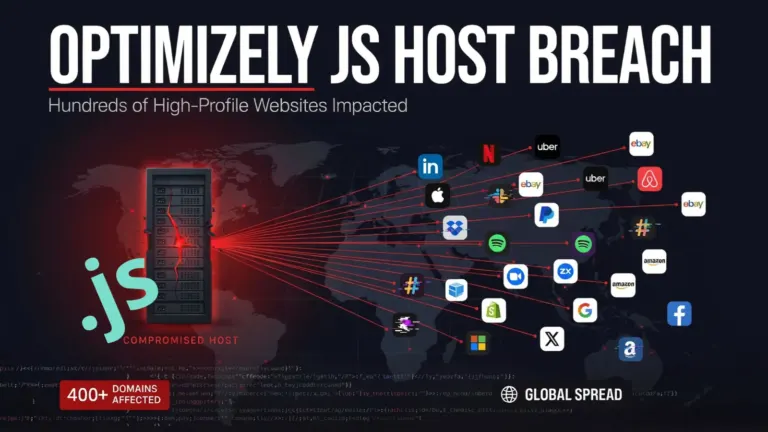
Poisoned Optimizely scripts swapped crypto addresses, skimmed cards and pushed Coruna and DarkSword iOS exploits for about 17…
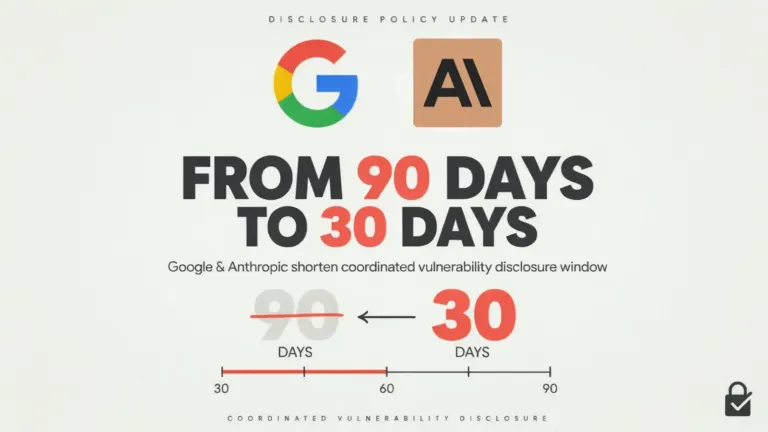
The AI company will reach a 30-day deadline a full year before Google Project Zero, and will chase…
The broken kernel also carries the fix for the remotely triggerable NoisyTCP crash, so admins who roll back…
A public exploit chains two 8.5-rated LibreOffice flaws to run Java code with no macro warning. Fixed in…
Only the browser installer writes the required WP_SECRETS_KEY, so sites upgraded from 7.1.4 get an API that returns…
The post itemises the bill stage by stage but names no CVEs, no affected subsystems and none of…
On-chain analysts tracked the stolen USDC being swapped into ETH within four minutes, while a higher $15.5 million…
NoisyTCP crashes cloud VMs in as little as 5 seconds through any open TCP port; fixes are in…
Patching is not enough: any Cisco FMC that ran vulnerable software after January 26 needs a compromise check…
Quick browser-based utilities. Check IMEI numbers, create Wi-Fi QR codes, decode JWTs, generate hashes, run DNS lookups, and more without installing anything.