npm Worm Hits keyv and cacheable, Spreads to 400 Packages
A self-propagating worm tore through the npm registry on Tuesday morning, trojanizing the widely used keyv…
We couldn't find any blog articles matching your search. Try searching for other cybersecurity topics or keywords.
A self-propagating worm tore through the npm registry on Tuesday morning, trojanizing the widely used keyv…
Attackers compromised the official Redhat cloud services npm namespace on June 1, 2026, injecting a sophisticated…
Security researchers at Socket have uncovered an active supply chain attack that poisoned 34 packages and…
The world’s largest code-hosting platform just became the victim of its own ecosystem. On May 20,…
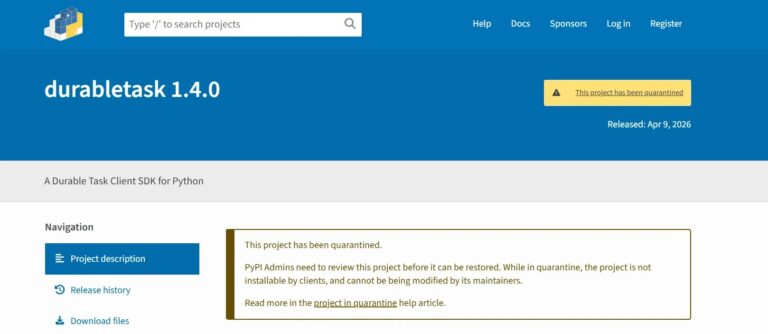
TeamPCP has quietly poisoned yet another trusted developer package — and this time the target was…
A self-propagating worm has torn through the TanStack JavaScript ecosystem, publishing 84 malicious versions across 42…

JDownloader, one of the most widely used free download managers with millions of users across Windows,…
If you’re building, training, or shipping AI models with PyTorch Lightning, check your installed version immediately…