Google has made AndroidX Security State 1.1.0 and Security State Provider 1.0.0 stable, allowing Android apps and Mobile Device Management (MDM) tools to check a device’s security patch status for each component. The Android Developers Blog announced the release on 17 September 2026, calling the single Security Patch Level (SPL) date apps rely on today “coarse, monolithic.”
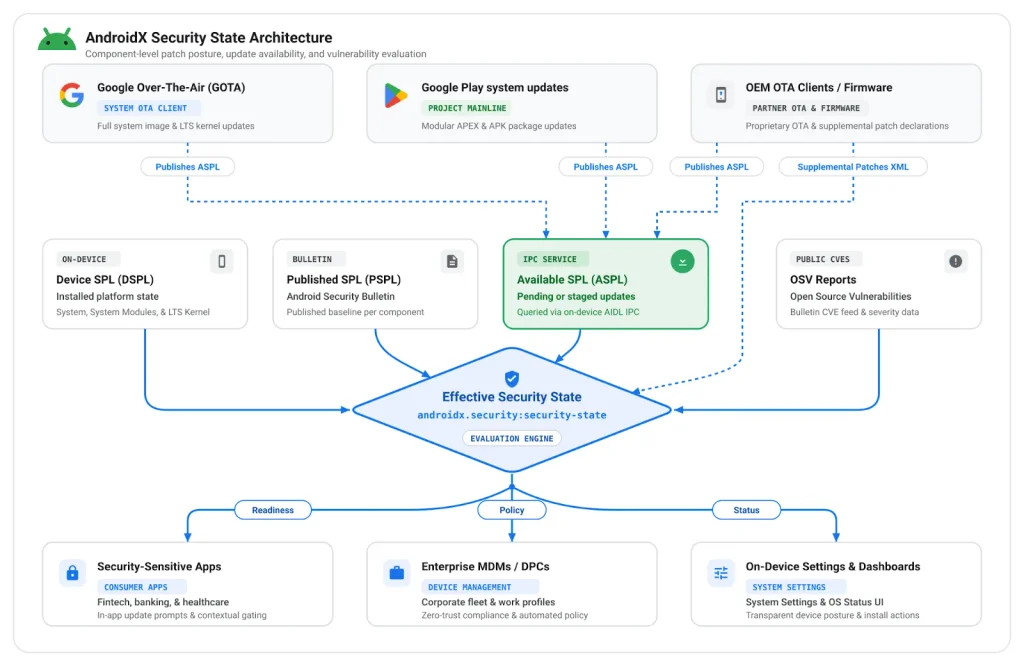
AndroidX Security State 1.1.0 reports three things separately for the Android system, the Google Play system update modules, and the kernel: the patch installed, the patch Google has published, and any newer patch waiting to be installed. The library can also confirm whether specific CVEs (publicly cataloged vulnerabilities) are fixed on the device. Both libraries were added to Google’s Maven repository on 9 September 2026, according to the AndroidX release notes.
What Are DSPL, PSPL, and ASPL?
DSPL, PSPL, and ASPL are the three patch levels AndroidX Security State reads for each component.
| Patch level | What it reports | Source |
|---|---|---|
| Device SPL (DSPL) | Patch installed and running | Device properties, no network call |
| Published SPL (PSPL) | The latest patch in the Android Security Bulletin | Bulletin data |
| Available SPL (ASPL) | Patch ready to install | IPC query to on-device update clients |
AndroidX Security State measures kernel patches using Long-Term Support (LTS) versions, such as 6.1.91, rather than monthly dates. If a monthly bulletin has no fixes for a component, the library still credits that component as current, Google said.
How Will Banking and MDM Apps Use It?
Google says a banking app can compare DSPL with ASPL before a high-value payment and require the user to install a pending update first. The same app can confirm that critical NFC and Bluetooth fixes are installed before allowing tap-to-pay. MDM apps can send employees to System Settings to finish a staged update instead of blocking the device.
What Changed Before the Stable Release?
AndroidX Security State entered alpha on 12 June 2024 and never shipped a stable 1.0.0, according to the release notes. Google pulled its update-availability APIs in January 2025. That capability returns in 1.1.0 through queryAllAvailableUpdates() and fetchAvailableSecurityPatchLevel().
Security State 1.1.0 trusts only update providers that hold the READ_PRIVILEGED_PHONE_STATE permission, which stops unprivileged preloaded apps from spoofing update data. CVE reports now default to the Open Source Vulnerabilities (OSV) endpoint at android-api.osv.dev.
Also Read
Which Devices Report Pending Updates?
Google Play system updates already report ASPL on devices with Google Mobile Services (GMS), and Google Over-The-Air (GOTA) is onboarded, according to Google. As of 19 September 2026, Google is still onboarding OEM update clients. Android 17 lets OEMs declare backported fixes above the SPL through a Supplemental Patches XML file, and the libraries pass that information to apps.
What Should Developers Do Now?
App and MDM developers add androidx.security:security-state:1.1.0 and follow Google’s device security state guide. OEMs add androidx.security:security-state-provider:1.0.0 and implement UpdateInfoService to publish ASPL.

Community Discussion
Join the conversation. Ask questions, share solutions, and help others.
Be the first to start the discussion!